
Microsoft Defender
Overview
The Microsoft Defender integration allows autobotAI to connect with Microsoft's unified enterprise defense suite, enabling automated security operations across your endpoints, cloud workloads, identities, and applications. Microsoft Defender for Endpoint (MDE) — together with Microsoft Defender XDR — provides rich threat intelligence, advanced hunting capabilities, automated investigation and response (AIR), and a centralized view of your organization's security posture.
By integrating Microsoft Defender with autobotAI, you can automate incident triage, isolate compromised devices, enrich alerts with threat context, trigger remediation workflows, and dramatically reduce mean time to respond (MTTR) to security threats.
This guide provides instructions for setting up the Microsoft Defender integration in your autobotAI account. By completing this process, you will connect your Microsoft Defender tenant and its security data to the platform.
Prerequisites
Before starting, ensure you have:
- An active Microsoft Defender for Endpoint or Microsoft Defender XDR subscription (Plan 1 or Plan 2 / E5).
- A Microsoft Entra ID (Azure AD) App Registration with appropriate API permissions.
- The following credentials from your App Registration:
- Tenant ID
- Client ID
- Client Secret
Instructions for creating an App Registration and granting the required permissions can be found in the Additional Information section.
Steps to Set Up Microsoft Defender Integration
Step 1:
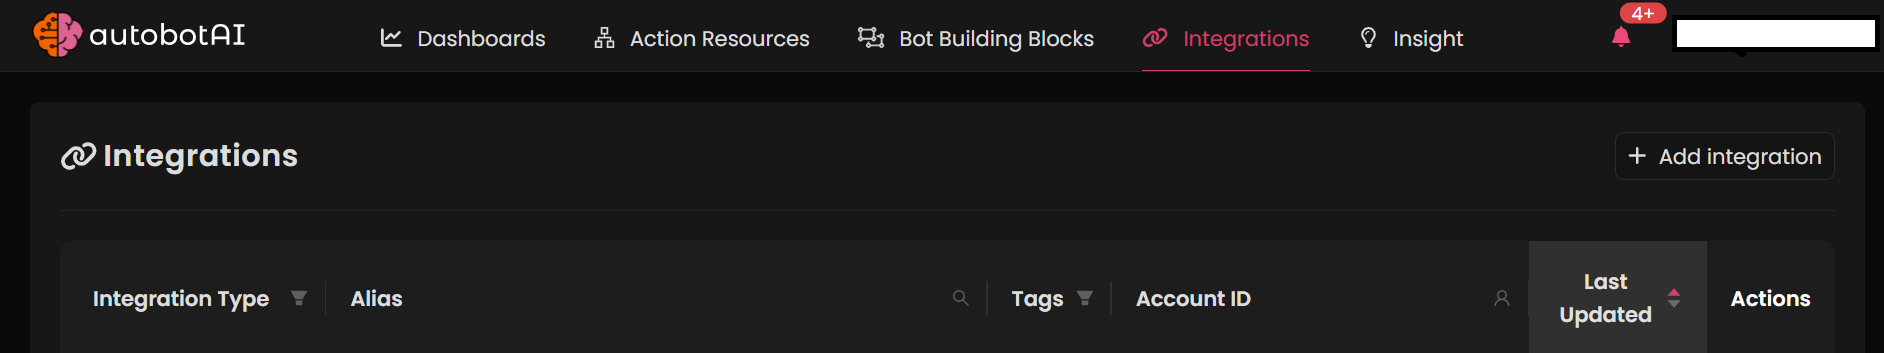
Navigate to the Integrations page by selecting Integrations from the menu. Click the + Add Integration button in the top-right corner to view available integrations.
Step 2:
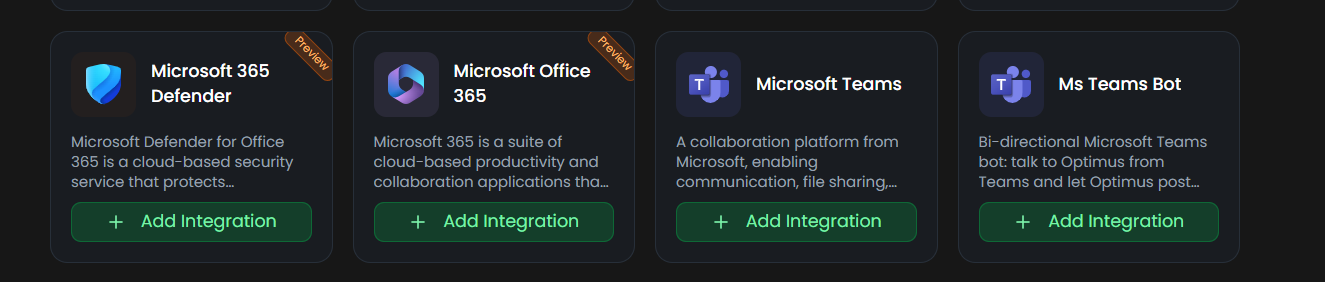
From the list, under the Security Tools section, select Microsoft Defender + Add to initiate the integration setup.
Step 3:
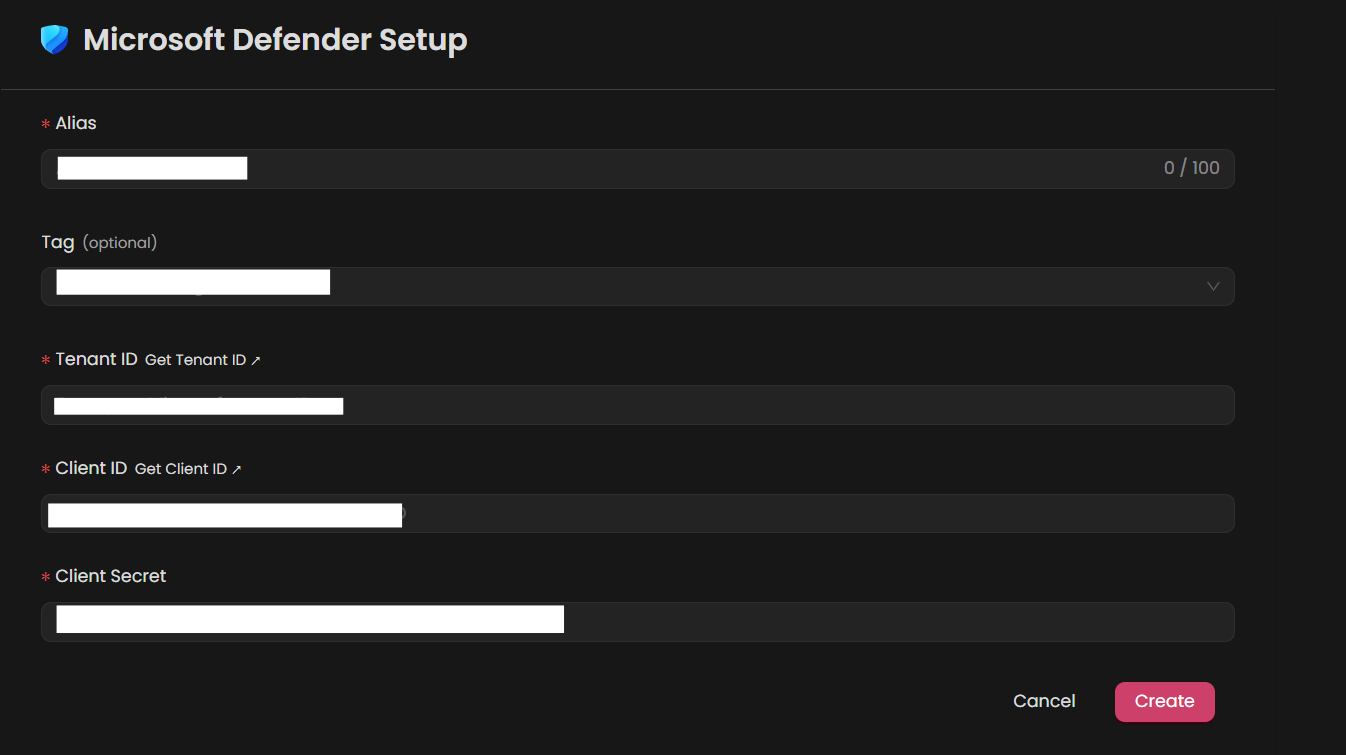
Fill in the required fields as follows:
Note: Fields marked with an asterisk (*) are mandatory.
- Alias: Provide a meaningful name or alias for this integration.
- Tag (Optional): Choose a tag to help organize the integration.
- Tenant ID: Enter your Microsoft Entra ID (Azure AD) Tenant ID.
- Client ID: Enter the Application (Client) ID from your App Registration.
- Client Secret: Enter the Client Secret value generated from your App Registration.
Verify the information, then click Create to complete the integration.
Step 4:
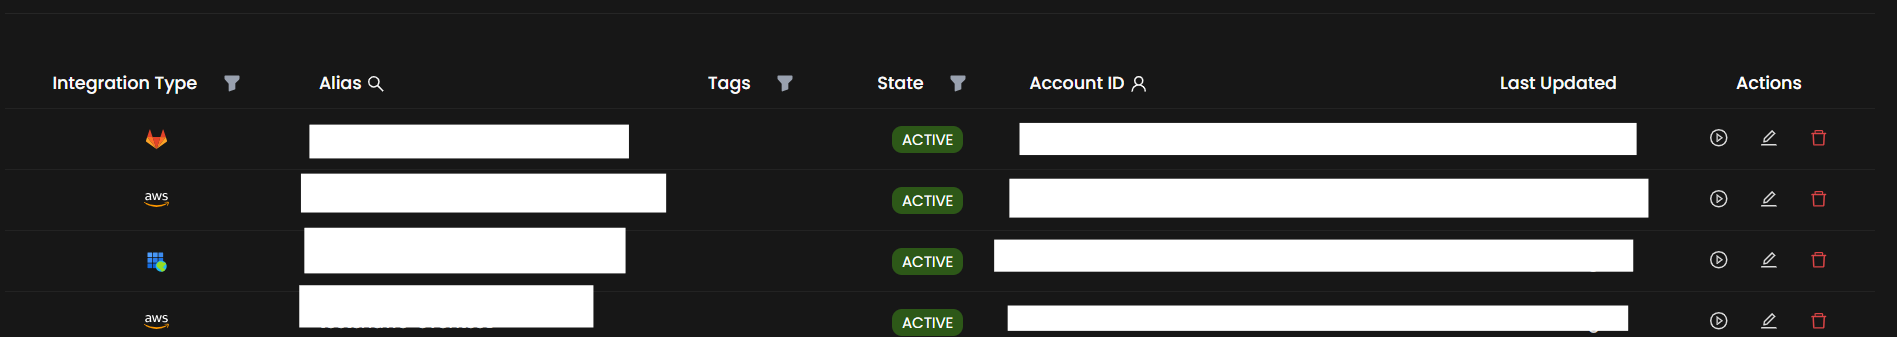
After the integration is successfully created, locate it under Integrations. Click on the three dots on the left side and select Test to ensure your integration is properly configured with autobotAI.
Additional Information
Required API Permissions
Your Entra ID App Registration must have the following Application permissions (not Delegated) granted and admin-consented:
| Permission | Type | Description |
|---|---|---|
Alert.Read.All | Application | Read all alerts from Microsoft Defender |
Alert.ReadWrite.All | Application | Read and update alerts |
Machine.Read.All | Application | Read all machine/device information |
Machine.Isolate | Application | Isolate a machine from the network |
Machine.RestrictExecution | Application | Restrict application execution on a machine |
Machine.CollectForensics | Application | Collect forensic investigation package |
Incident.Read.All | Application | Read all Defender XDR incidents |
Incident.ReadWrite.All | Application | Read and update Defender XDR incidents |
AdvancedHunting.Read.All | Application | Run advanced hunting queries |
How to Create an App Registration and Retrieve Credentials
-
Log in to Microsoft Azure Portal:
- Go to https://portal.azure.com and sign in with Global Administrator or Security Administrator credentials.
-
Create a new App Registration:
-
Navigate to Microsoft Entra ID → App registrations.
-
Click New registration.
-
Enter a name (e.g.,
autobotAI-Defender), select Accounts in this organizational directory only, and click Register. -
After creation, note the Directory (Tenant) ID and Application (Client) ID from the app's Overview page.
-
-
Grant API Permissions:
- Navigate to API permissions → Add a permission.
- Select APIs my organization uses and search for WindowsDefenderATP.
- Select Application permissions and add the permissions listed in the table above.
- Click Grant admin consent to apply the permissions.
-
Create a Client Secret:
- Navigate to Certificates & secrets → New client secret.
- Enter a description, select an expiration period, and click Add.
- Copy the secret value immediately — it will not be shown again.
-
Enter Credentials in autobotAI:
- Paste the Tenant ID, Client ID, and Client Secret into the corresponding fields on the autobotAI integration form to complete the setup.
Once the integration is configured, test it to confirm autobotAI can successfully communicate with your Microsoft Defender environment.