
A workspace is a self-hosted deployment of autobotAI in your own AWS account and region. Your agents, workflows, credentials, execution history and audit trail stay in your account, while your agents still reach AWS, Azure, Google Cloud, Kubernetes, on-premises systems and your security tools.
Deployment uses a CloudFormation stack and typically takes 30 to 45 minutes.
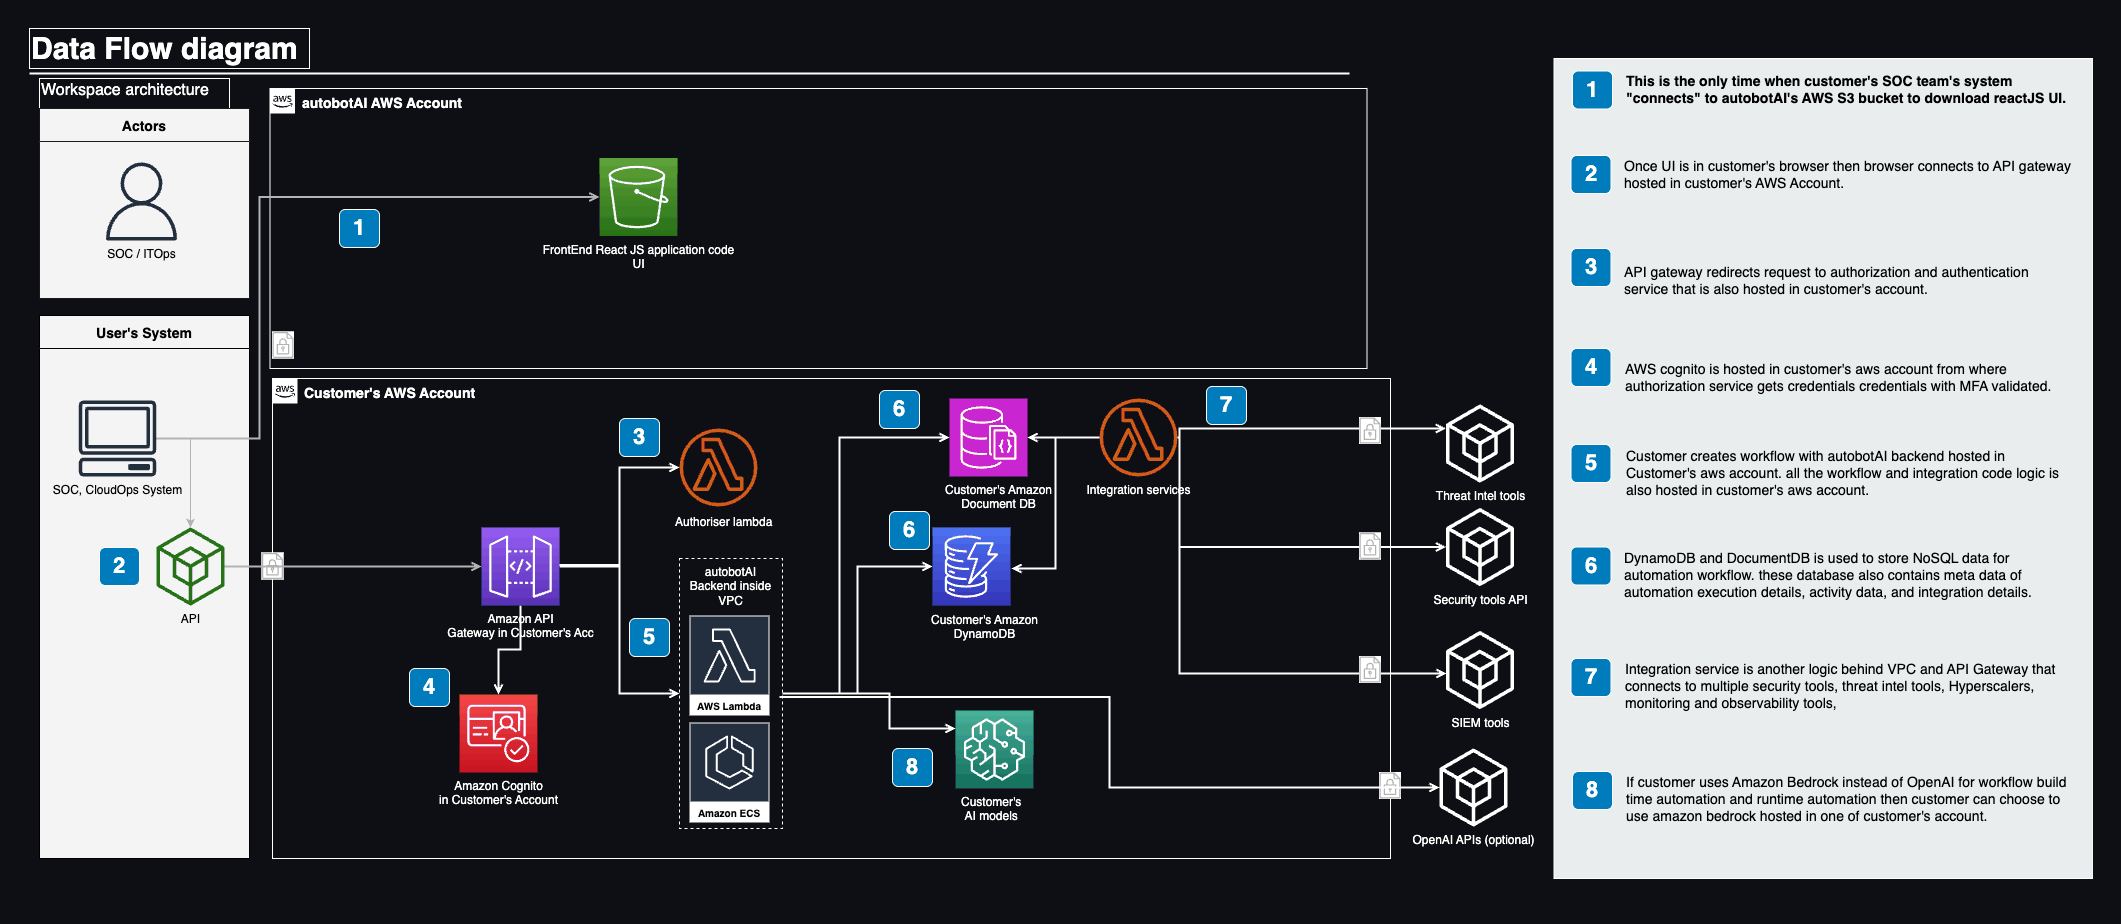
For how each component is secured and what stays in your account, see Architecture and security.
Prerequisites
Before deploying your Workspace, ensure you have the following:
-
✓ An active AWS account
-
✓ An active autobotAI subscription on AWS Marketplace
-
✓ Access to an IAM User with Administrator privileges >
Security Warning:
Do not use your AWS account root user to deploy or operate autobotAI Workspace.
Instead, create and use an IAM user with AdministratorAccess for initial deployment and restrict to least privilege for ongoing operations. -
✓ A valid Administrator Email to be used as the Workspace’s primary login
Plan network reach first: if the workspace will be connected to your data center or other VPCs by VPN, Direct Connect, transit gateway or peering, for example to penetration-test internal apps, its VPC range must not overlap those networks. Custom ranges are an Enterprise option chosen before deployment. See Hybrid and private networks.
Note: If your AWS account is new or hasn’t used ECS before, make sure the ECS service-linked role is available.
You can check and create it here.
Supported AWS Regions
autobotAI Workspace supports the following AWS regions for deployment:
- US East (N. Virginia) -
us-east-1 - Asia Pacific (Mumbai) -
ap-south-1
Need another region? More AWS regions are being added. Contact support to confirm availability in your region before you deploy.
Deployment Steps
Step 1: Log into AWS
Open a new browser tab and sign in to your AWS Console using an IAM user with admin permissions.
Note: Make sure your AWS account is subscribed to autobotAI on the Marketplace before deploying a Workspace. Subscription ensures access to deployment and platform services.
Step 2: Open autobotAI Dashboard
In a separate tab:
-
Go to autobotAI Dashboard
-
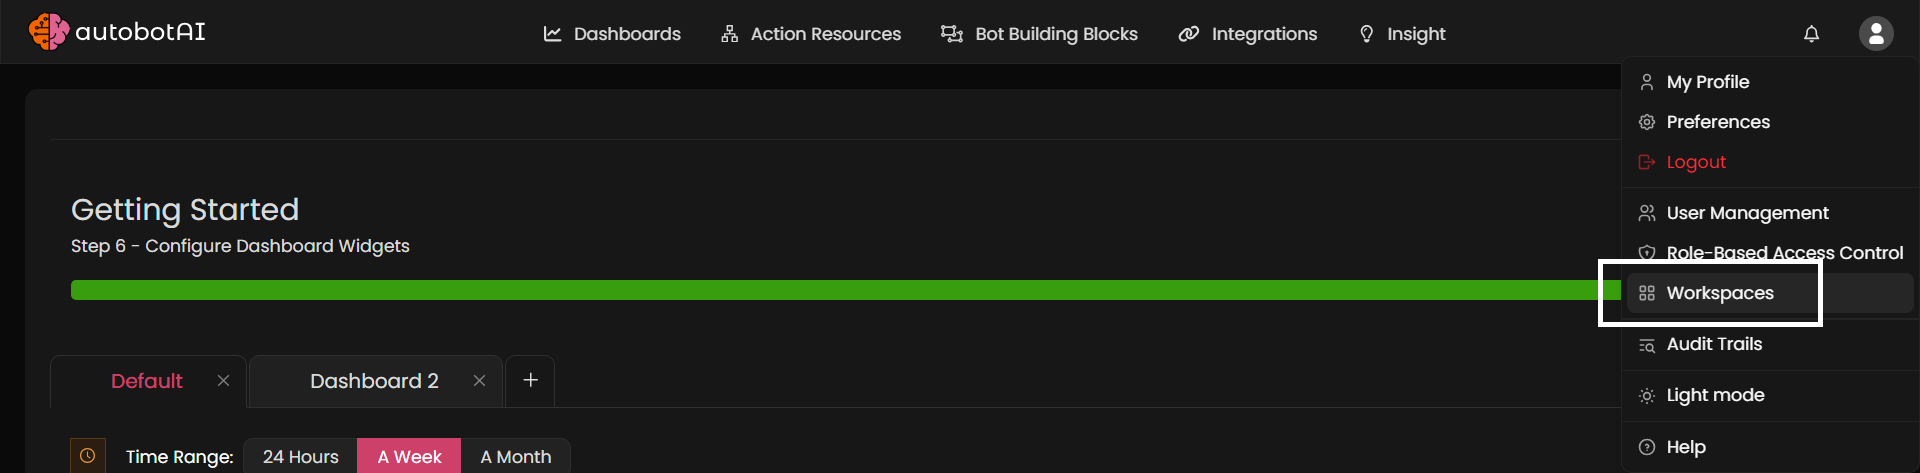
Click your Profile Icon in the top-right corner
-
Select Workspaces from the dropdown
Don’t have an account yet? Learn how to set up your autobotAI account
Step 3: Create a New Workspace
Click on + New to create a new Workspace.
Fill in the form with the following details:
| Field | Description |
|---|---|
| AWS Account ID (12 digits) | The AWS account where the Workspace will be deployed |
| Administrator Email | This user will be the Workspace admin and receive login credentials via email |
| AWS Region | Select the AWS region where you'd like the Workspace to be deployed. |
| Workspace Name | Provide a unique name for your Workspace (used as a subdomain) |
| Workspace Version | Select the version of the Workspace to deploy (default: latest) |
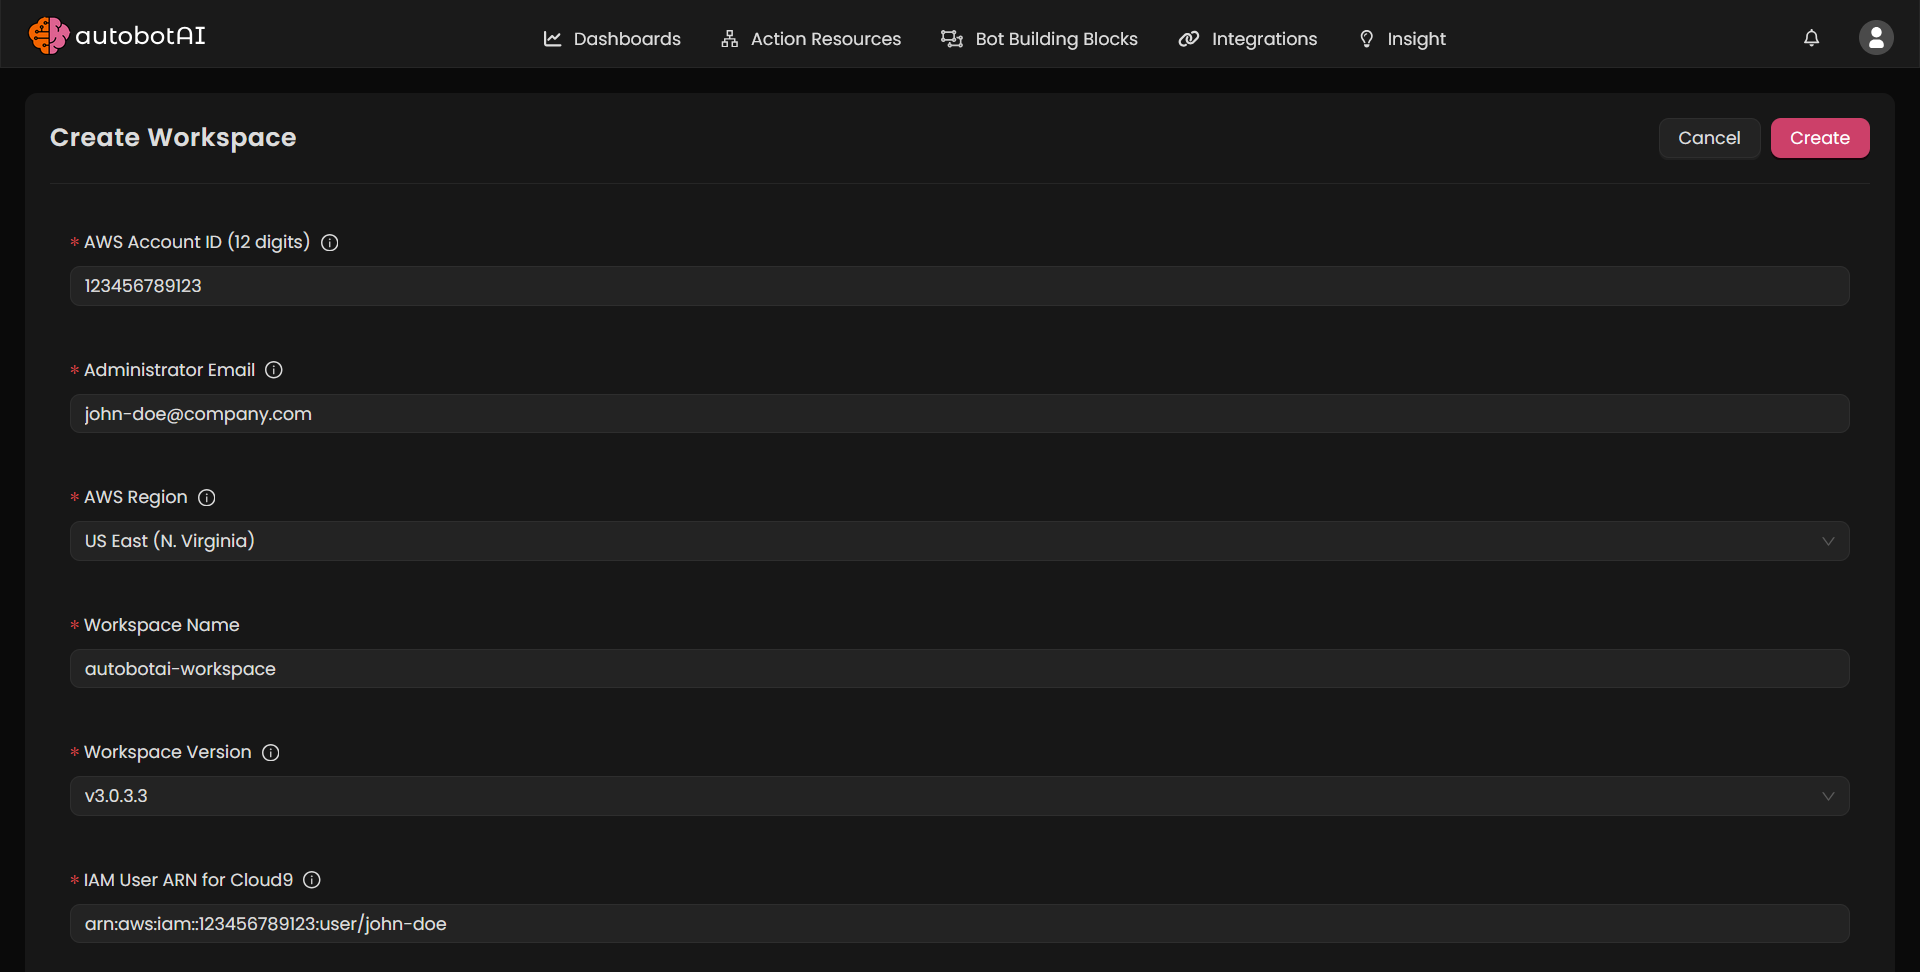
Click Create to continue.
Step 4: Launch the AWS Stack
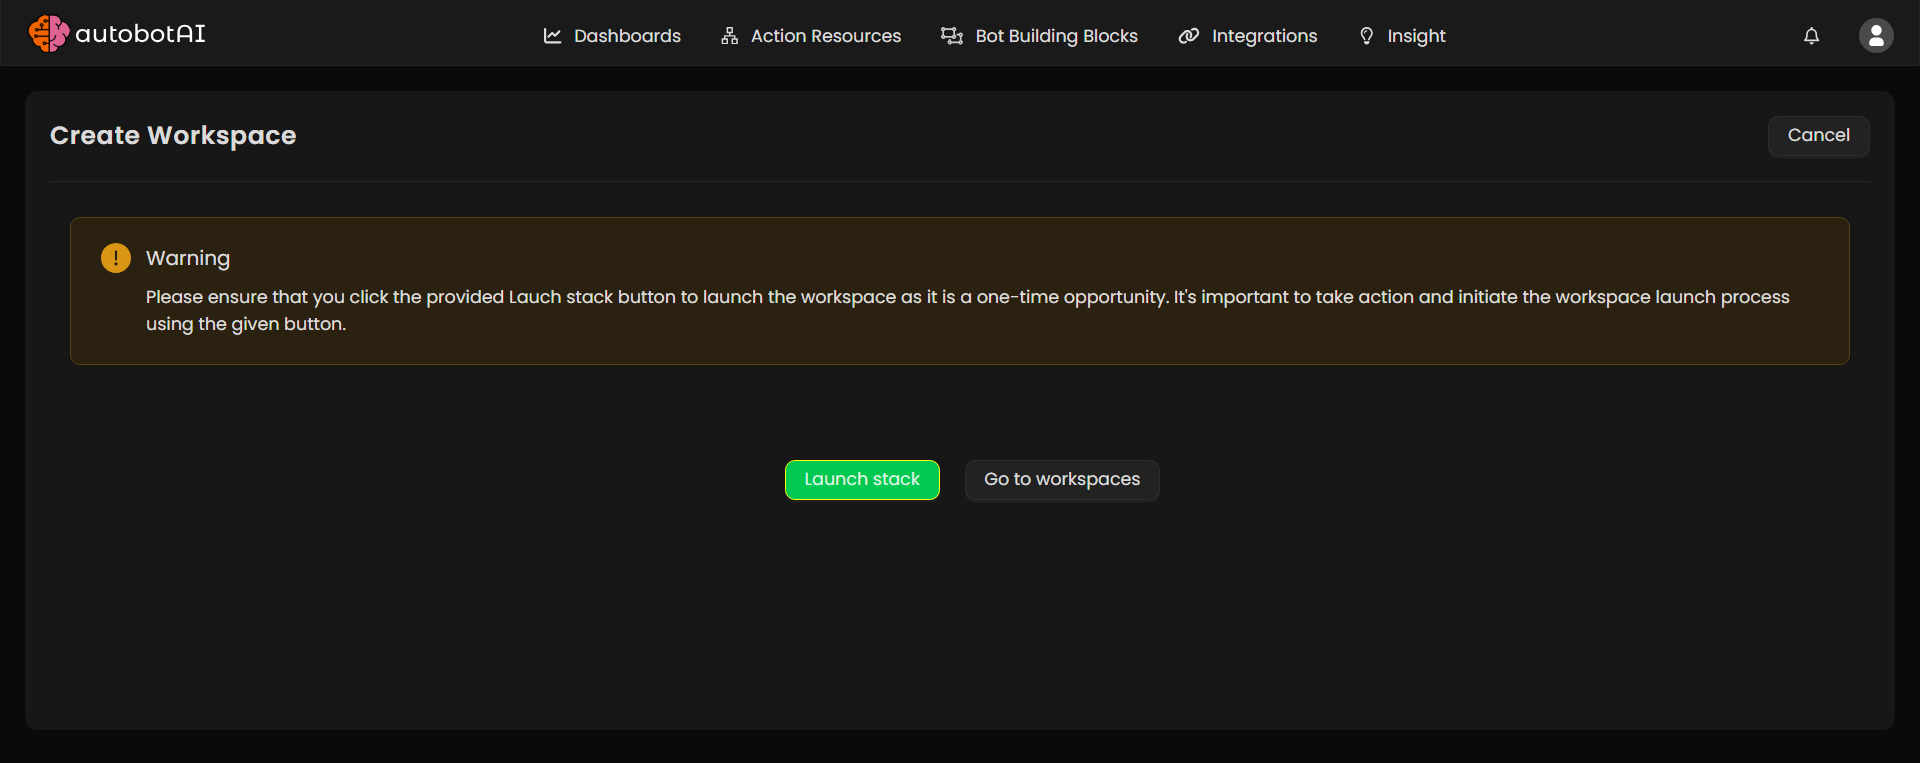
Once you submit the form, you'll be prompted to launch the AWS CloudFormation stack.
-
Click Launch Stack. This opens the CloudFormation Console in a new tab
-
Scroll to the bottom of the page and check the acknowledgment box
-
Click Create Stack to begin deployment
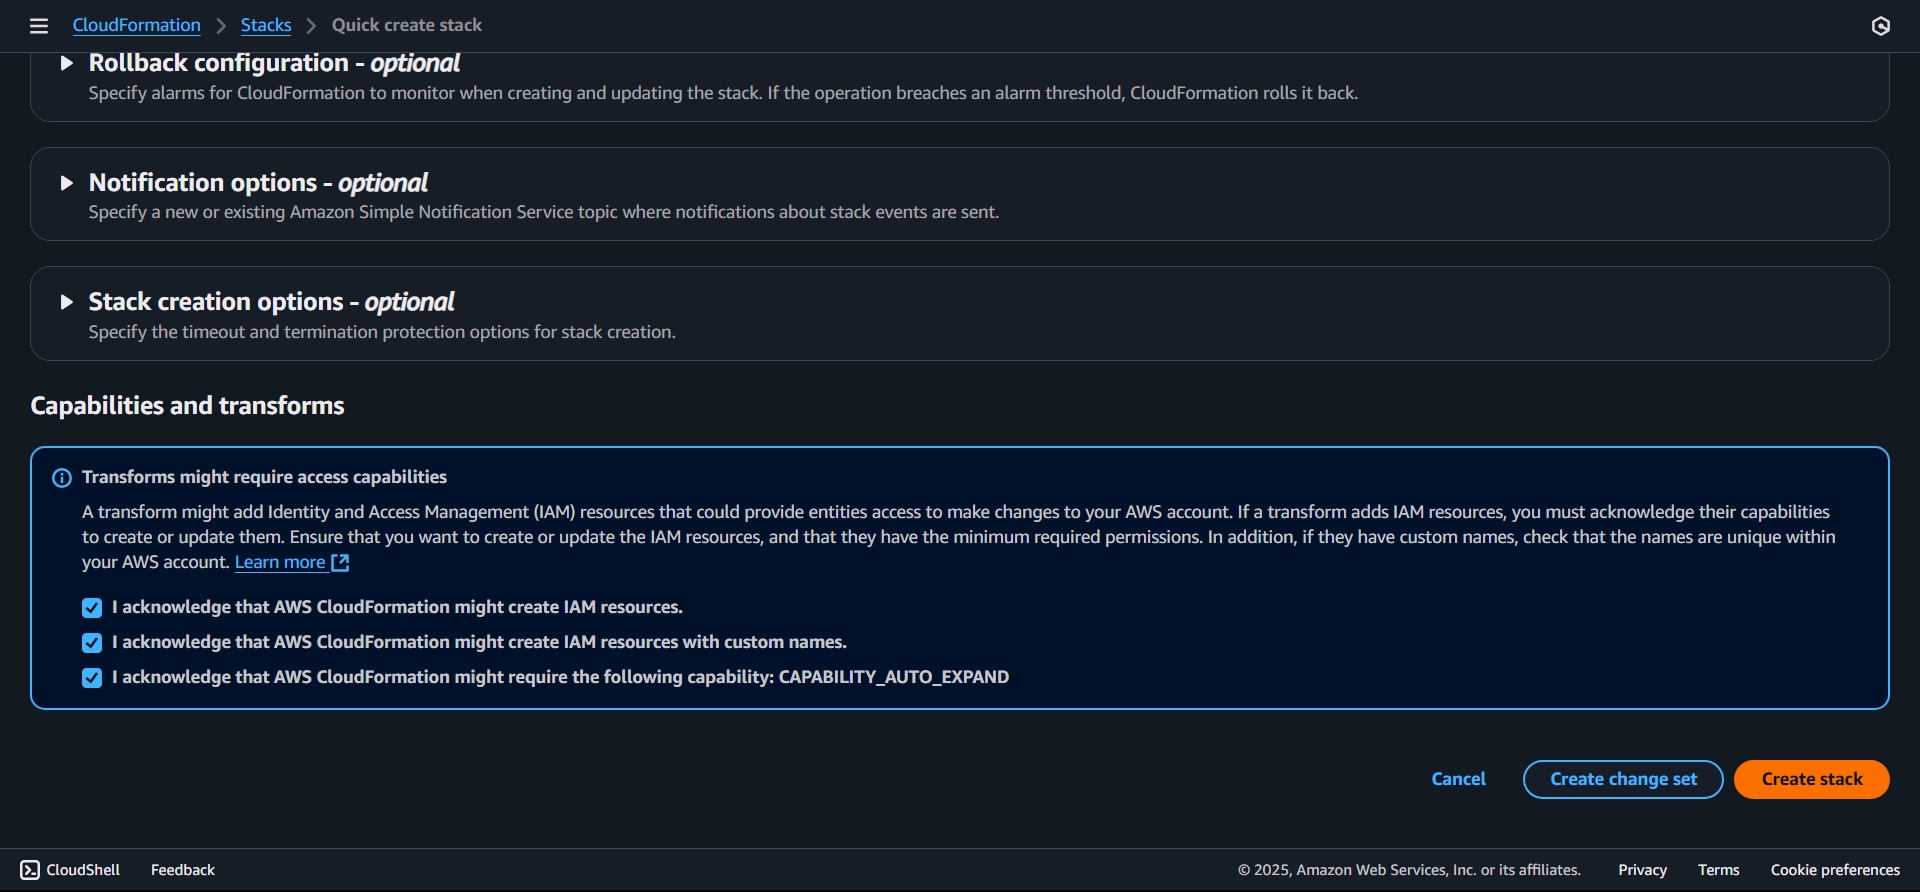
Important: Do not change any of the parameter values. They are auto-generated by autobotAI
Step 5: Wait for Deployment
Estimated Deployment Time
The typical deployment time for autobotAI Workspace is 30–45 minutes, assuming the following:
- AWS account and IAM prerequisites are pre-configured
- Network infrastructure (VPC, subnets) created by CloudFormation
- Database services (DynamoDB, DocumentDB) provisioning complete
- Compute services (Lambda, ECS) deployment and container image pulls
- API Gateway and Cognito setup
- Testing and validation of basic workspace health
Note: Deployment time may vary by AWS region and network connectivity.
Caution: Large enterprise customizations (e.g., custom VPC CIDR planning) may extend deployment time.
Step 6: Verify Your Administrator Email
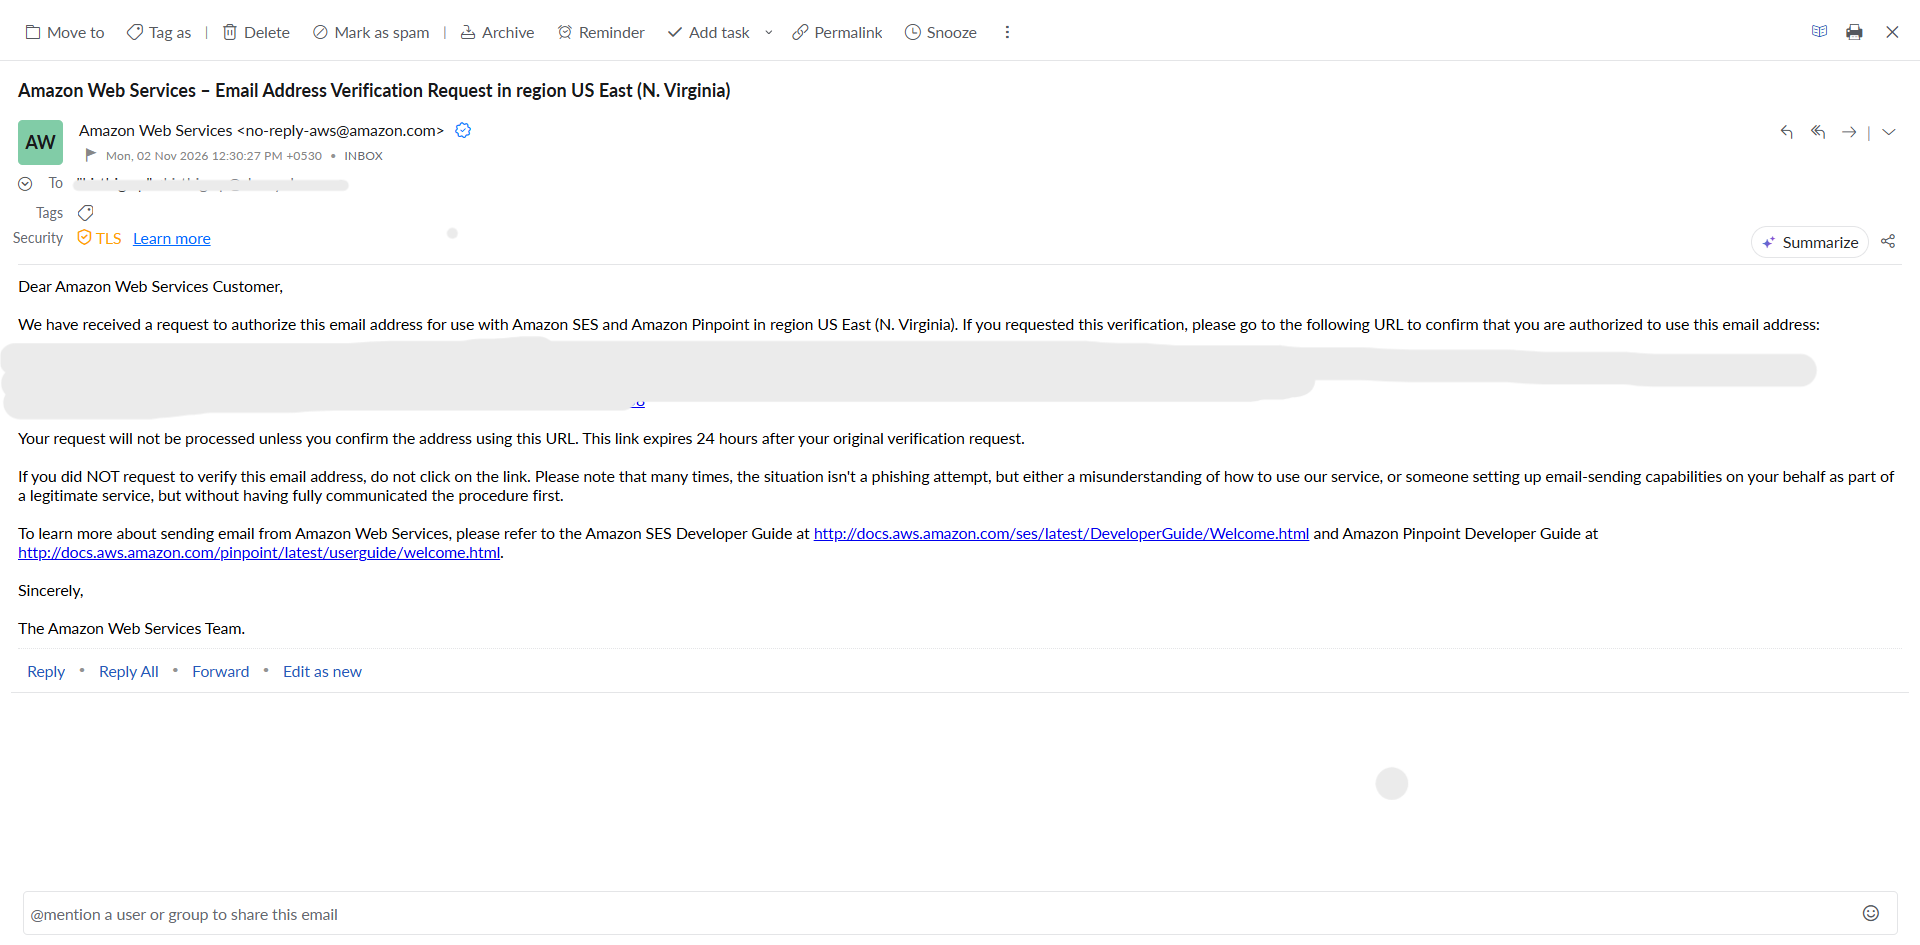
During deployment, your Workspace registers the Administrator Email as a sender in Amazon SES (Simple Email Service) in your AWS account. Your Workspace uses this address to send you notifications, starting with your welcome email.
While the stack deploys, the Administrator Email receives these emails:
| Sender | What to do | |
|---|---|---|
| Amazon Web Services – Email Address Verification Request in region … | no-reply-aws@amazon.com | Click the verification link. The link expires after 24 hours. |
| AWS Notification - Subscription Confirmation | no-reply@sns.amazonaws.com | Click Confirm subscription to receive Workspace system alerts by email. |
| Your temporary password | no-reply@verificationemail.com | Keep it. You need it for your first login (see below). |
📌 Note: These emails come from AWS on behalf of your own AWS account. If you don't see them, check your spam or junk folder.
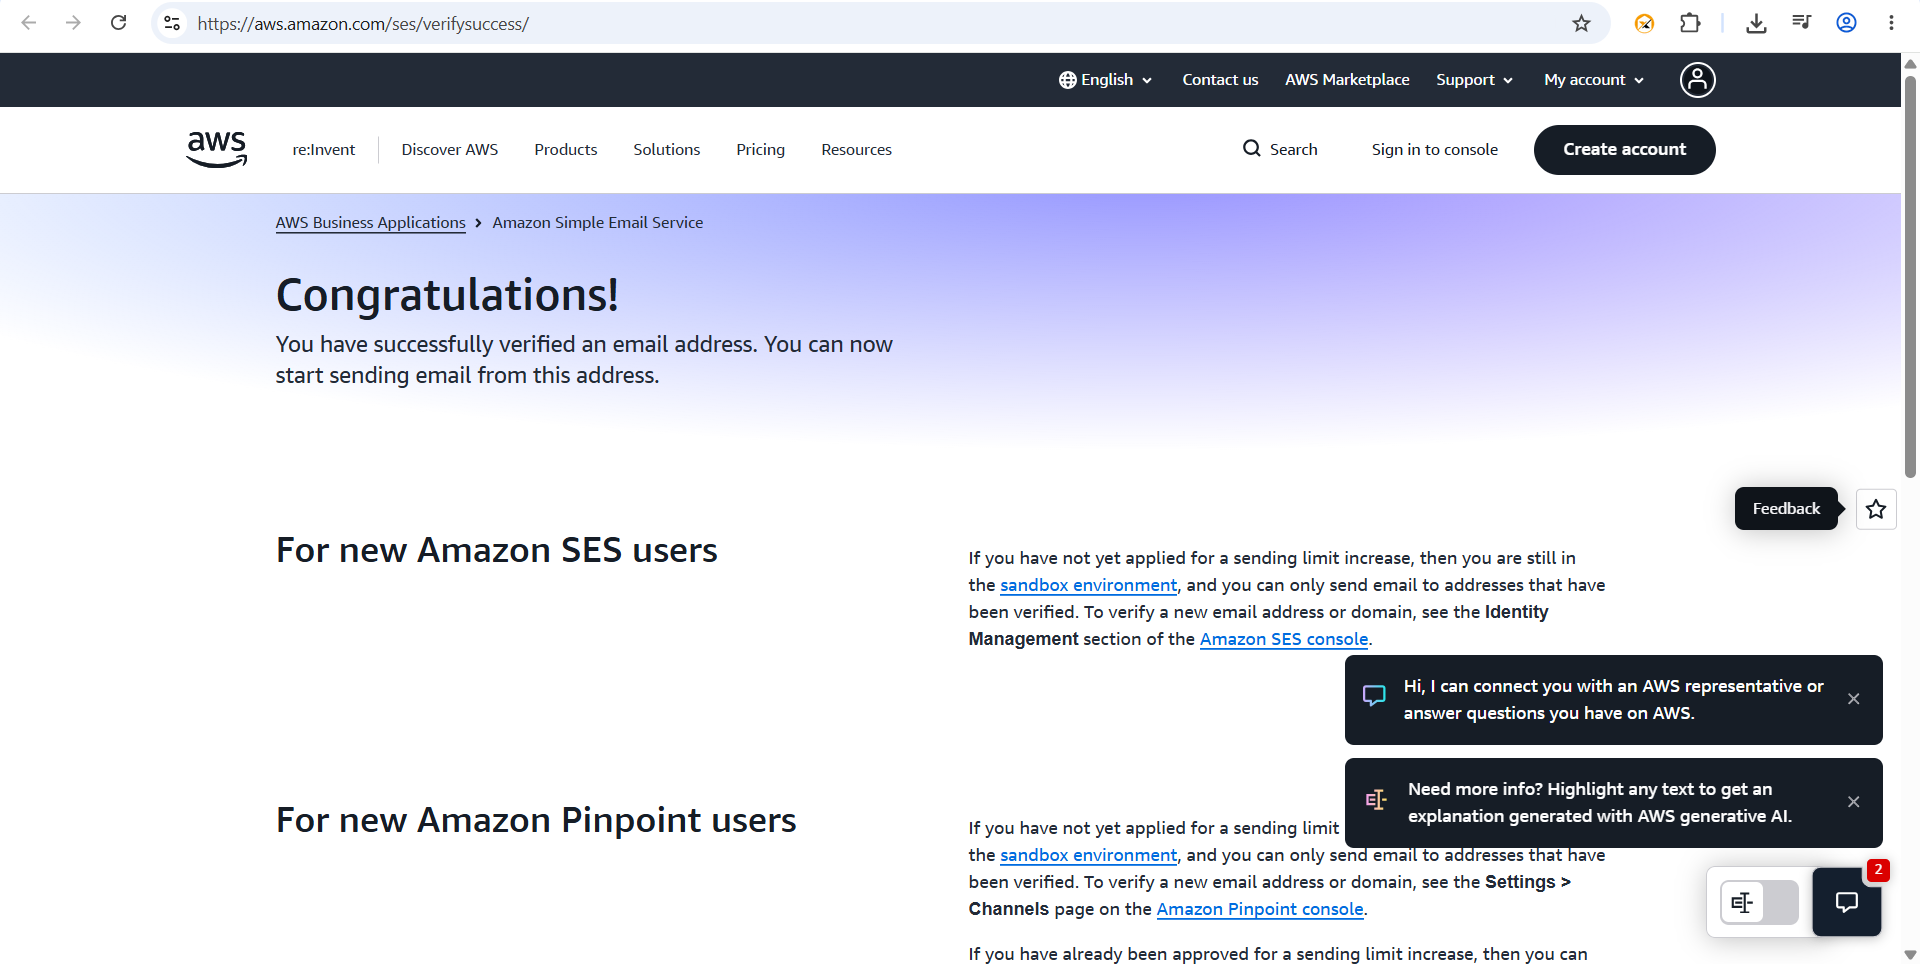
After you click the verification link, AWS shows a Congratulations! page confirming the address is verified.
Verification link expired?
If you didn't click the link within 24 hours, it no longer works. To get a new link, open AWS CloudShell in the Workspace region and run (replace the email address):
bashaws sesv2 delete-email-identity --email-identity admin@example.com
aws sesv2 create-email-identity --email-identity admin@example.com
A new verification email arrives within a few minutes.
Setting Up Workspace Credentials
Once your stack is deployed:
-
Go back to the Workspaces section on the autobotAI dashboard and wait for the Workspace status to change to "Running".
-
Click Actions → Go to Workspace next to your deployed Workspace.
-
You'll be redirected to the Workspace's dedicated subdomain
-
Log in using the temporary credentials sent to your administrator email
-
You'll be prompted to set a new password
-
Set up 2-Factor Authentication (2FA) using apps like Authy or Google Authenticator
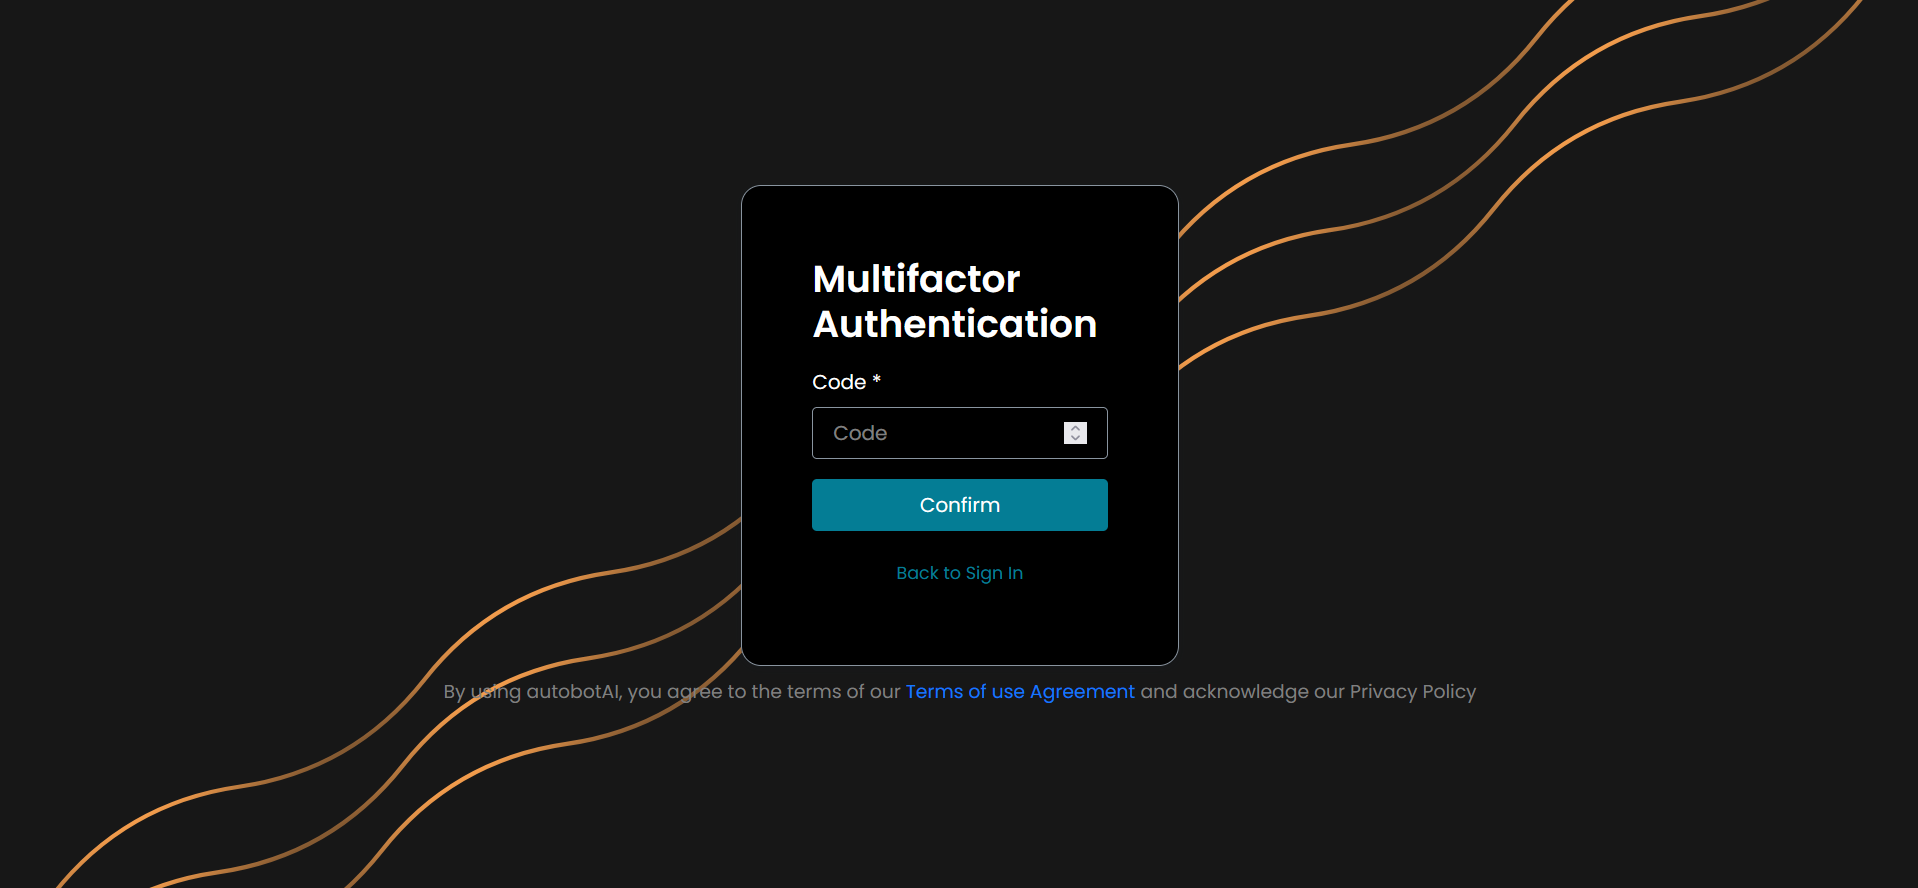
Backup Reminder: Save your 2FA secret in a secure location.
If you lose access to your authenticator and secret backup, you’ll need to redeploy the Workspace. -
Enter the OTP from your authenticator to complete the setup
-
You'll be redirected to the autobotAI Workspace homepage
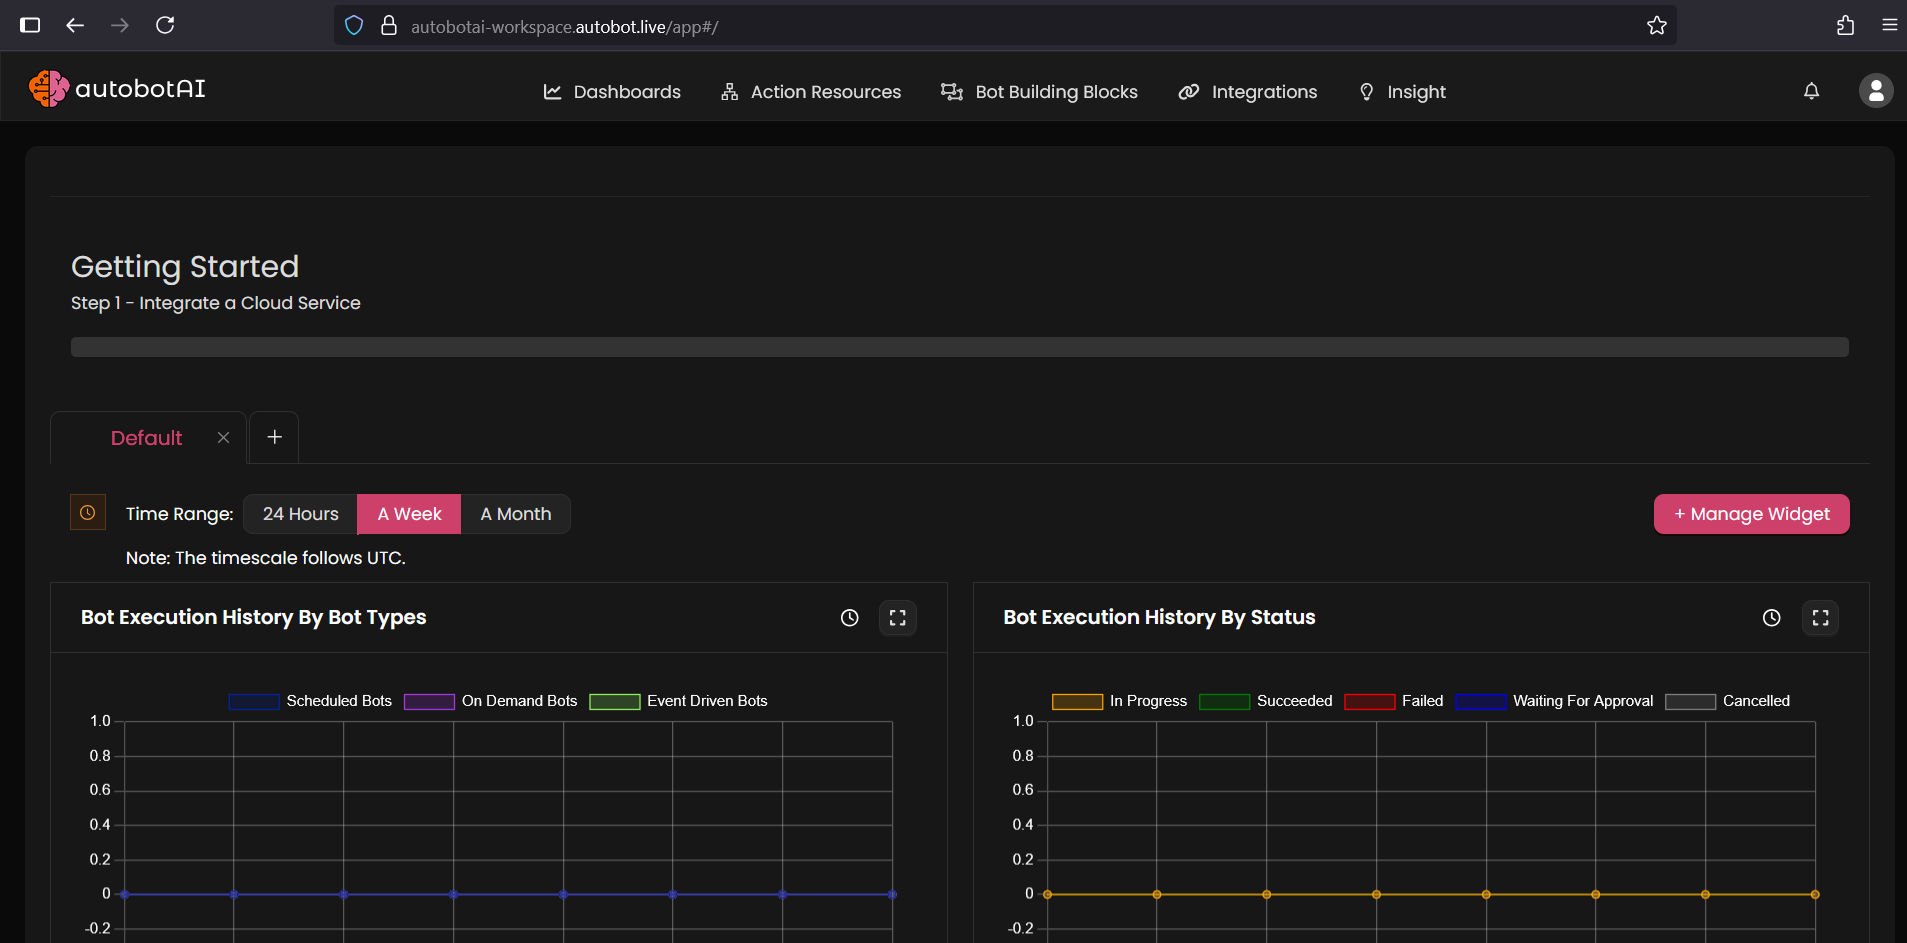
-
Check your inbox for the Welcome to autobotAI email. It is sent from your own Administrator Email through Amazon SES, which confirms that email notifications from your Workspace work.
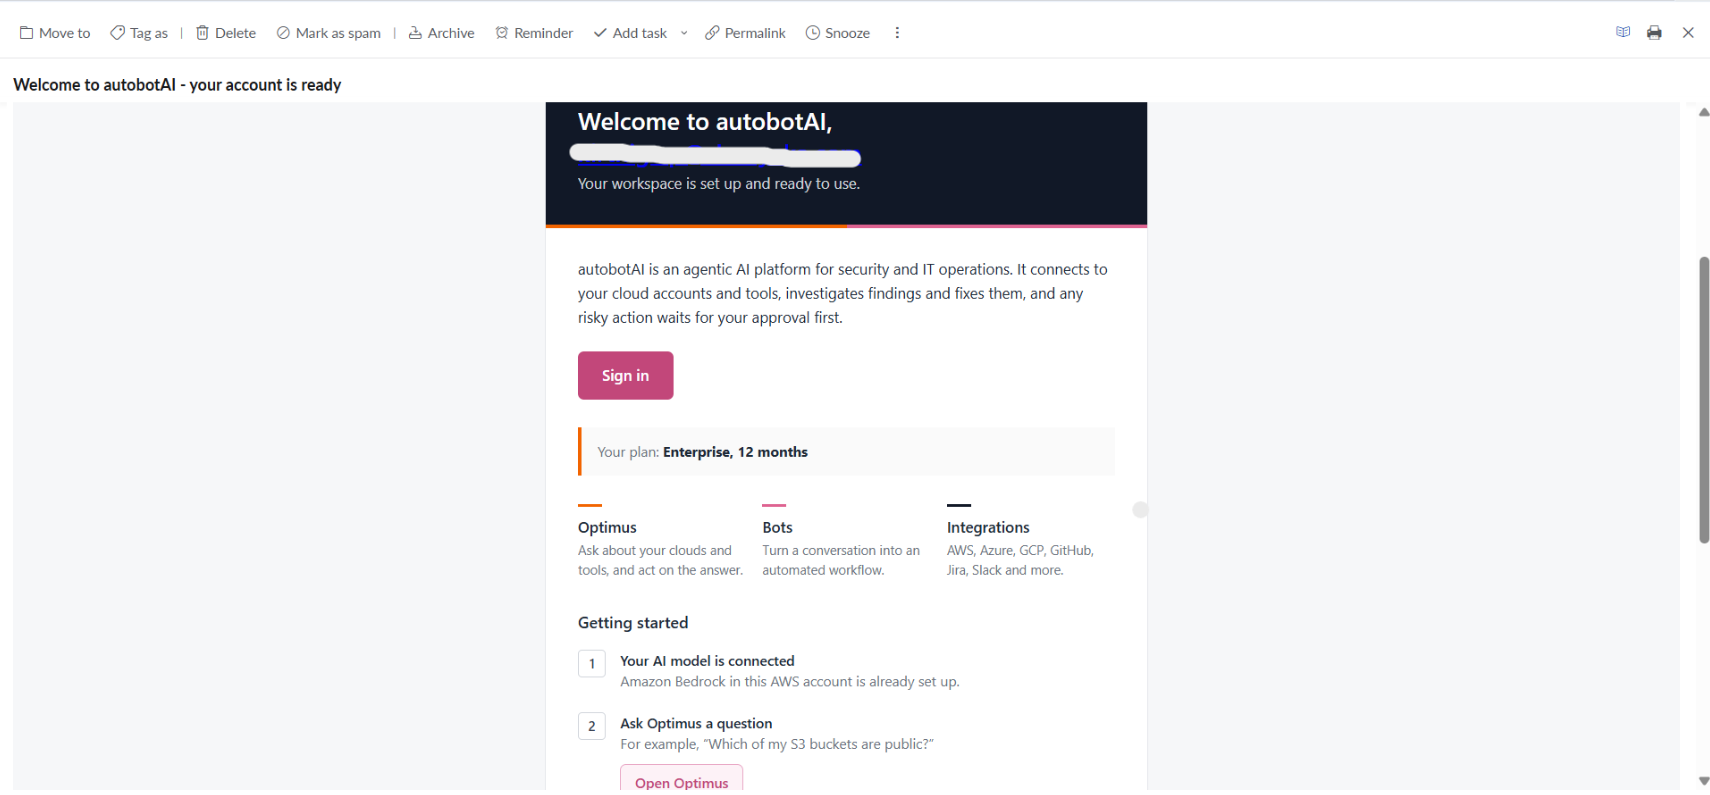
📌 Didn't get the welcome email? It's sent only after the Administrator Email is verified (Step 6). Verify it, then log out and log in again. The email is sent on your next login.
Check ECS Service-Linked Role
In some newer AWS accounts, or where ECS hasn't been used before, the ECS service-linked role may be missing.
This role is required for successful Workspace deployment.
To check and create it, follow these steps using AWS CloudShell
1. Open CloudShell
From the AWS Console, click the CloudShell icon in the top navigation bar.
2. Check if the ECS service-linked role exists:
Run following command:
bashaws iam get-role --role-name AWSServiceRoleForECS
If you see an error like NoSuchEntity, the role does not exist yet.
3. Create the ECS service-linked role (if needed):
Run following command:
bashaws iam create-service-linked-role --aws-service-name ecs.amazonaws.com
Once this role is created, you can continue with launching the CloudFormation stack.
What the stack exposes
The workspace keeps its compute and data in private subnets. Only these resources face the internet:
| Resource | Exposure | Controls |
|---|---|---|
| API Gateway (REST API) | HTTPS endpoint | Every request is checked by a Lambda authorizer against Amazon Cognito in your account |
| AppSync Events API | HTTPS endpoint | Pushes live updates, such as run progress, to the web app |
| NAT gateway | Public subnet, outbound only | Lets private compute reach your tools and model provider. Accepts no inbound connections |
Note:
- Lambda functions, ECS tasks and DocumentDB run in private subnets without public IPs.
- S3 buckets the workspace creates are not publicly accessible.
- Review the public endpoints with your security team, and consider AWS WAF or IP restrictions. See Add your own guardrails.
IAM roles
The stack creates IAM roles for its Lambda functions, ECS tasks and setup steps, each scoped to the resources that component uses. Workspace resource names contain -live-<workspace name>, so you can find them in the IAM console.
- Review the roles after deployment.
- Don't change their policies unless autobotAI support asks you to: upgrades expect them as deployed.
- After deployment, remove any temporary administrator access you granted for the deployment, as described in the workspace reference.
Next steps
Your workspace is ready for your first agents.
- Connect a model. Amazon Bedrock keeps model calls inside your AWS account. See Connect your AI models.
- Connect your tools, such as AWS, GitHub, Slack and the Kubernetes agent. See How integrations work.
- Build your first workflow. Continue the Quickstart from step 3.
- Share the architecture with your security team: Architecture and security and the workspace reference.
If the deployment fails, see Troubleshoot a deployment.