From risk found to risk closed.
A practical guide to agentic security operations: why detection stopped being the bottleneck, why bolt-on agents repeat the script-sprawl mistake, and how teams run an agent factory with people in control.
 autobotAIWHITEPAPER · 2026
From risk found
to risk closed.
The practical guide to agentic security operations, with people in control.
The whole argument, in one map.
Detection is solved
Every tool now ships AI for finding risk. Finding fast is no longer the constraint.
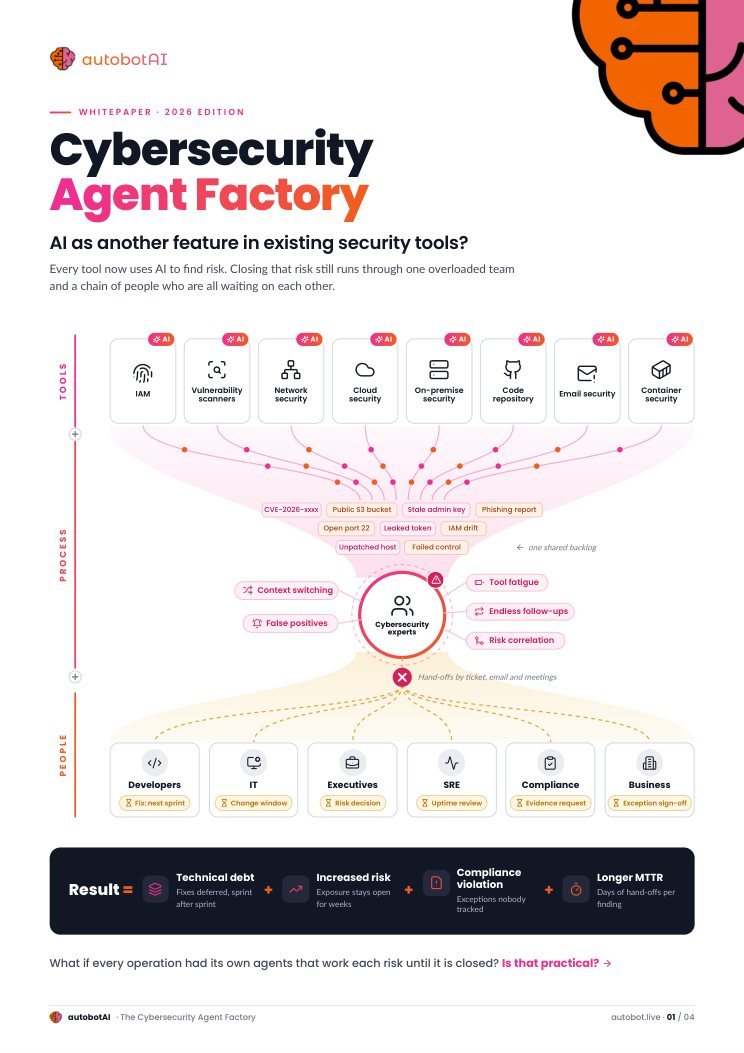
The closure gap
Found in seconds, closed in weeks: where the time actually goes.
Why bolt-on agents fail
Sprawl 2.0, the integration tax, and agents that stop at detection.
The agent factory
Design, build, tune and run your own agent swarm on one integration layer.
Workflows and deep agents
When to fix the steps, when to let an agent plan, and how to mix both.
Bounded autonomy
A0–A3 tiers set by each action’s risk, governed through Trust, Risk, Audit, Policy and Safety.
The shared harness
Knowledge base, operations memory, asset graph, skill catalog and guardrails, kept live.
Measuring closure
Task and risk registers, four treatment outcomes, and a four-week adoption plan.
Three pictures worth the read.
Typical manual timeline from autobotAI customer-workflow analysis. Same journey for a leaked secret, a risky access grant or a public bucket.
One agent per tool, nobody maintaining them. The script-sprawl story again.
Engineering spent wiring tools eats the budget meant for the security problem.
The agent finds and summarises, and the risk stays open.
Agent proposes. A person acts.
Agent prepares. A person approves, then it runs.
Acts inside scoped, capped, reversible guardrails. People notified and can revoke.
Risky capability removed at the credential layer, e.g. forensics can’t write.
“Autonomy is never the absence of governance. It’s governance moved earlier, into guardrails, scopes and reversibility, and proven continuously after the fact.”
One paper, four readers.
CISO
How to answer “are we secure?” with a live register instead of a quarterly deck.
SOC lead
Which steps to hand to agents first, and where people stay in the loop.
GRC
Evidence by default, exceptions tracked, and how autonomy is governed.
Security engineering
Workflows vs deep agents, the harness, and the cost of each choice.
Take it to your next planning meeting.
The ideas, the key figures and a four-week adoption plan you can lift straight into a proposal.
 Work email and company, and the PDF downloads straight away.